Infostealers infect computers and cellphones in a variety of ways. The most common methods are through pirated software, malicious email attachments, or deceptive links on social networks. They pose a silent threat but manage to harvest a lot of sensitive information from victims. Researcher claims to have confirmed leak with victims. Troy Hunt, who runs the Have I been pwned website (which aggregates leaked credentials), stated that he managed to confirm at least two cases. In one instance, leaked Gmail username and password were legitimate; in another, the person verified the list of sites they accessed – mostly adult content pages – and mentioned two other correct emails and passwords. There is no breakdown of how many legitimate logins and passwords are included in the leaked files. Contacted, Google mentions that this is not a unique case for Gmail and unfortunately, this type of malicious activity occurs. ‘These continuous updates of credential theft databases are not from a single, targeted attack on one person. Instead, attackers use various tools to gather credentials,’ the company stated.

Leak of 183 million logins includes Gmail accounts; learn how to check

-
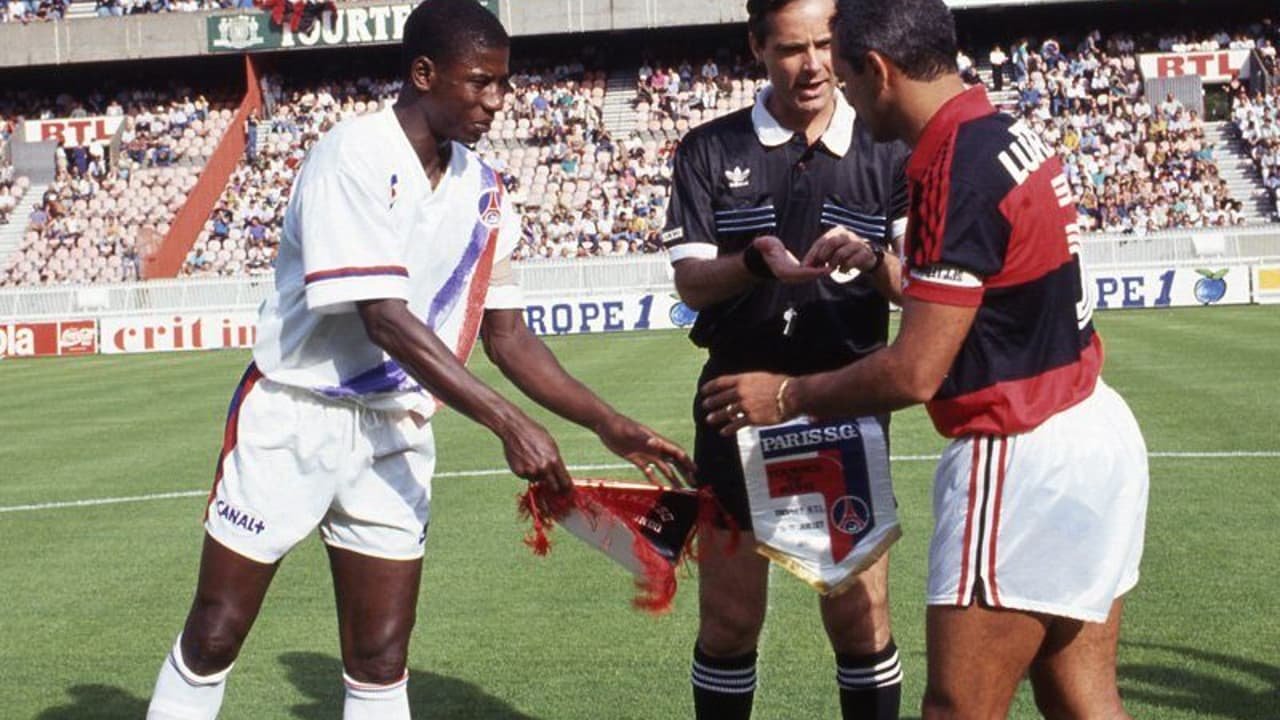
Flamengo and PSG have faced each other three times; check out their record
-
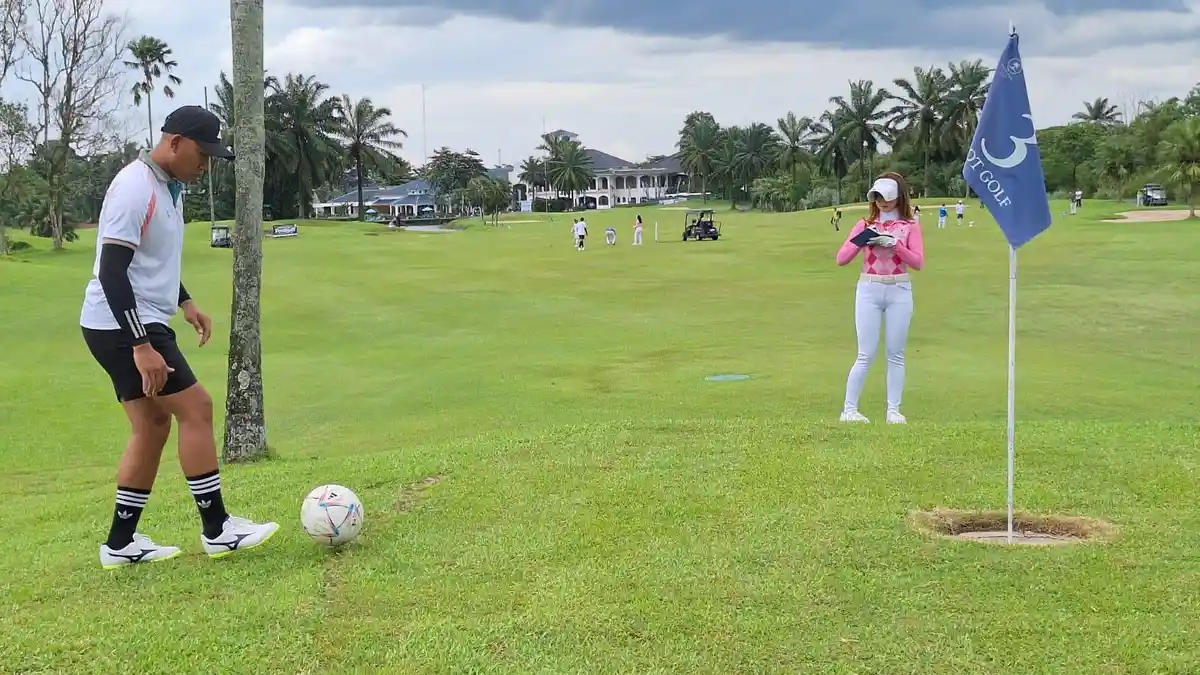
Indonesia Open Footgolf Tournament: Comedian Oki Rengga Admits Addiction, Wants to Become a Professional Athlete
-
Shameful Incident in Punjab! Landlord Rolls Tenant’s Daughter
-
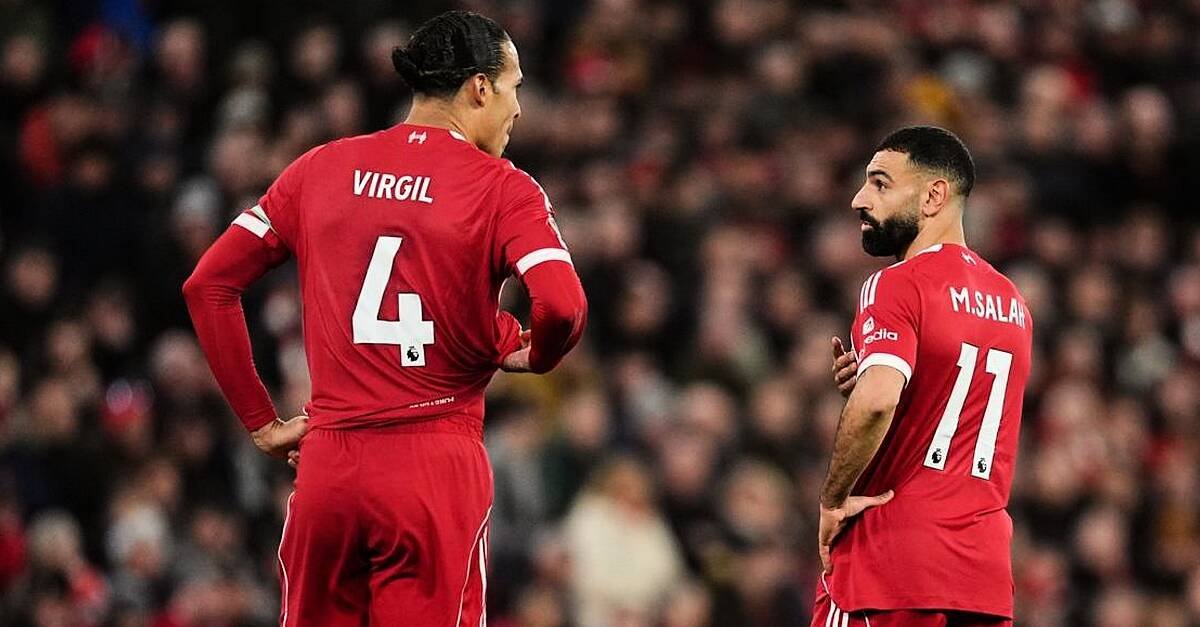
Virgil van Dijk Expresses Desire for Mohamed Salah to Stay at Liverpool
Deixe um comentário